The Gentlemen ransomware has been among the fastest-growing ransomware operations since the second half of 2025. Unlike automated campaigns that strike indiscriminately, its affiliates study the victim’s infrastructure, identify the security tools in use, and tailor the attack to overcome the defenses they find.
The group operates under a Ransomware-as-a-Service model, known as RaaS. In this setup, those behind The Gentlemen develop the ransomware, maintain the leak infrastructure, manage decryption keys, and provide tools to affiliates who carry out the intrusions.
The operation also uses double extortion. Before encrypting files, the criminals may copy confidential information and threaten to publish it if payment is not made. This means a company can face system downtime and a potential data breach at the same time.
Researchers have identified variants capable of targeting Windows, Linux, and VMware ESXi environments. In addition, the ransomware can stop processes related to virtualization, databases, enterprise applications, and backup software before starting encryption.
For an affected organization, understanding how the threat works is only the first step. It is also necessary to halt its spread, preserve evidence, analyze backups, and technically assess the possibilities for recovering data encrypted by The Gentlemen.
Digital Recovery has already recovered more than 10 TB in a real-world incident involving this ransomware.

What is The Gentlemen ransomware?
The Gentlemen is a ransomware operation that emerged in mid-2025. Initially, it appears to have run as a closed group before offering its ransomware to affiliates around September of the same year. Microsoft tracks the platform’s operators under the identifier Storm-2697.
Intelligence reports indicate that members of the operation may previously have acted as ArmCorp, an affiliate of the Qilin ransomware. This relationship should be understood as an assessment based on research and public information, not as an official confirmation about all participants in the group.
In the RaaS model, responsibilities are divided. The operators maintain the malware, the affiliate panel, the leak site, and the negotiation mechanisms. Affiliates are responsible for obtaining network access, moving through the infrastructure, stealing data, and executing the ransomware.
One factor that helped attract affiliates was the offer of a share of up to 90% of the amounts paid by victims. This percentage is higher than commonly observed in other ransomware programs, which tend to reserve a larger portion for the operators.
The group’s name and visual identity are inspired by the aesthetic associated with Guy Ritchie’s productions. However, the polished presentation is not its main differentiator. The danger lies in its ability to customize attacks, develop in-house tools, and change the intrusion method according to the defenses found in the company.
Why did The Gentlemen grow so quickly?
The Gentlemen’s growth is linked to the combination of a financially attractive program for affiliates and an advanced toolset provided by the operators.
Instead of providing only the encryptor, the group maintains capabilities for credential theft, network reconnaissance, lateral movement, and disabling security solutions.
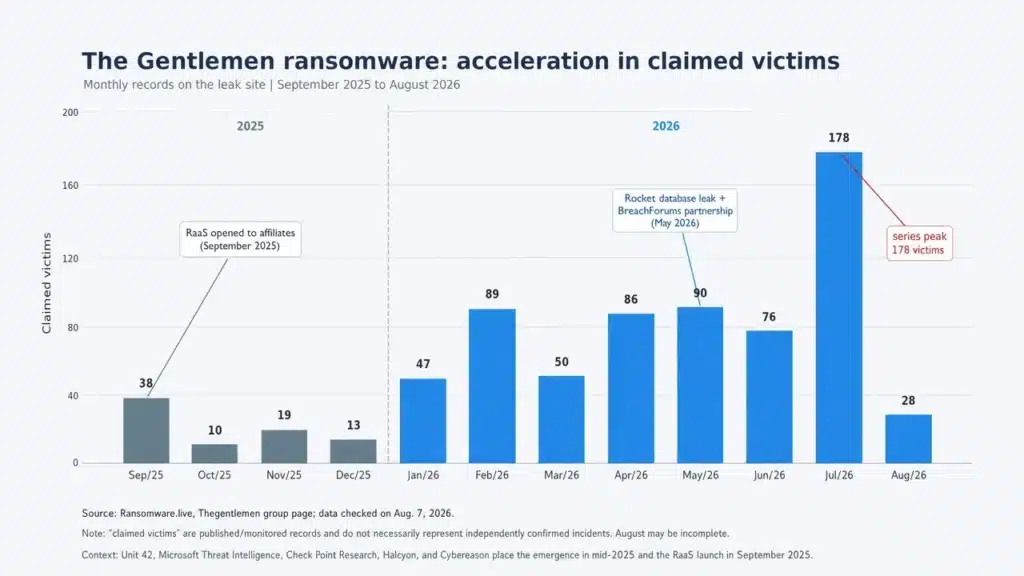
As of July 7, 2026, sources monitored by Unit 42 counted 580 claimed victims across 77 countries since the operation began. Of these, 103 were in the manufacturing sector. The number of claimed victims in the first half of 2026 was more than six times the figure recorded in the final months of 2025. These data represent organizations announced by the group and not necessarily all incidents that occurred or those independently confirmed.
The activity is not focused solely on the United States. ESET research identified victims in Southeast Asia, South America, and Western Europe, including Brazilian organizations. In Brazil, cases were observed in education, healthcare, technology, manufacturing, agribusiness, construction, and business services.
Another relevant factor is adaptability during the intrusion. When a given tool is blocked, affiliates can modify scripts, swap tools, or use different mechanisms to continue the operation. As a result, each attack may present a distinct combination of tools and techniques.
How does a The Gentlemen ransomware attack unfold?
The encryption phase usually represents the final stage of the attack. Before that, the intruders need to enter the network, obtain elevated privileges, locate important assets, and weaken the organization’s defenses.
Initial access
Initial access can occur through:
- vulnerabilities in firewalls, VPNs, and other edge devices;
- administration interfaces exposed to the internet;
- stolen or leaked credentials;
- brute-force attacks;
- remote access without multi-factor authentication;
- services provided by initial access brokers;
- compromised vendor or third-party accounts.
Research by Unit 42 linked the group to exploitation of exposed devices, compromised credentials, brute-force attacks, and collaboration with intermediaries that sell access to corporate networks.
This variety means there is no single vulnerability or method responsible for all attacks. The entry point depends on the conditions found in each organization and the skills of the affiliate involved.
Infrastructure reconnaissance
After entering the network, the intruders seek to understand how the environment is organized. Tools such as Advanced IP Scanner and Nmap may be used to locate servers, workstations, domain controllers, and administrative interfaces.
Reconnaissance also covers Active Directory. Operators look for privileged accounts, administrative groups, virtualization servers, backup systems, and devices that store critical information.
This stage helps the criminals identify the systems that must be compromised to cause the greatest possible impact.
Credential theft and privilege escalation
Credentials obtained during the intrusion allow attackers to broaden their control over the infrastructure. Administrative accounts can be used to access shares, change settings, create tasks, run programs remotely, and reach different network segments.
ESET also associated a credential-stealing tool called OxideHarvest with affiliates of the group. The presence of this capability shows that account access remains an important part of The Gentlemen’s operational ecosystem.
When the domain is compromised, the intruders can use group policies, the NETLOGON share, and other legitimate administrative mechanisms to distribute files and commands simultaneously.
Disabling antivirus and EDR
One of the operation’s most important characteristics is the development of GentleKiller, a toolset created to stop EDR solutions and other security mechanisms.
ESET identified at least eight GentleKiller variants that abuse vulnerable or malicious drivers. This technique is known as Bring Your Own Vulnerable Driver, or BYOVD. The attacker installs a driver with a known vulnerability and uses its privileges on the system to terminate security processes.
The group also integrates external or leaked tools such as HexKiller, ThrottleBlood, and HavocKiller. The operators adapt these resources, apply obfuscation, and make them available to affiliates.
This structure reduces the need for each affiliate to develop their own evasion method. It also allows the group to react quickly when new proof-of-concepts or vulnerable drivers are disclosed.
Beyond these specialized tools, the ransomware can execute commands to:
- disable Microsoft Defender real-time monitoring;
- add files and volumes to exclusion lists;
- disable Windows Firewall;
- delete shadow copies;
- clear system logs;
- erase PowerShell histories;
- remove records related to RDP connections.
The variant analyzed by Microsoft used vssadmin and wmic to delete Volume Shadow Copies and wevtutil to clear security, system, and application logs.
Data theft
Before executing encryption, affiliates may copy documents, personal data, financial information, databases, contracts, intellectual property, and other files considered sensitive.
These data are transferred to external infrastructure and used as leverage. Even when a company has backups capable of restoring systems, the threat of publication keeps the extortion active.
Technical recovery of files therefore does not automatically eliminate the risks associated with leakage. The organization must also investigate which information was accessed and assess applicable legal and regulatory obligations.
Propagation across the network
Self-propagation is one of The Gentlemen ransomware’s main technical differentiators.
When executed with the propagation parameter, the malware looks for reachable devices and attempts to deploy the encryptor on each of them. It can use credentials provided by the operator or reuse the authentication token from the compromised session.
In the sample studied by Microsoft, the malware created a hidden SMB share, prepared the infected computer to distribute the executable, and enumerated workstations, servers, and domain controllers.
After that, it attempted several remote execution methods, including:
- PsExec;
- WMIC;
- creating scheduled tasks;
- creating services;
- PowerShell Remoting;
- WMI via PowerShell;
- copying the executable via the administrative C$ share;
- execution from an SMB share prepared by the malware.
The ransomware made up to 21 remote execution attempts per identified device. The methods were executed independently, increasing the likelihood that at least one would succeed in delivering the file to the remote machine.
This behavior brings The Gentlemen closer to a worm-like threat. A single compromised machine can become a distribution point for other systems reachable within the network.
File encryption
The Windows variant analyzed by Microsoft was developed in Go and protected with the Garble obfuscator. It uses a combination of Curve25519 and XChaCha20 encryption, generating cryptographic information specific to each file.
The ransomware also allows the operator to define different speed levels. Files smaller than or equal to 1 MB may be fully encrypted. In larger files—such as databases, virtual machine images, and large archives—the threat can encrypt three separate regions.
Depending on the parameter chosen, the total amount encrypted in a large file can vary by approximately 0.9% to 27%. Even a small percentage can be enough to damage headers, indexes, metadata, and essential structures.
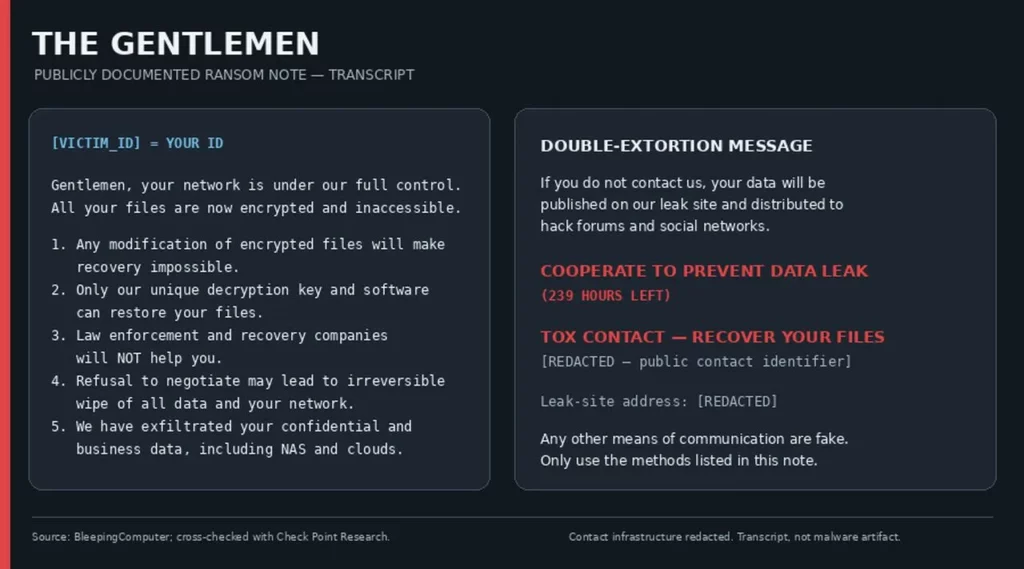
In the sample documented by Microsoft, files received the extension: .umc16h
The ransom note was created with the name: README-GENTLEMEN.txt
These elements are useful indicators but should not be treated as universal patterns. Extensions, notes, keys, and settings may change between versions and campaigns.
Which systems can be affected?
The Gentlemen is not just a threat to documents stored on users’ computers. Its tools were developed to target entire corporate environments.
Windows servers and workstations
The variant analyzed by Microsoft can encrypt local disks, mapped drives, and network shares accessible via UNC paths.
With administrative credentials, the ransomware can be distributed to workstations and servers, run with system privileges, and reach files that would not be available to a normal user.
Active Directory
Compromise of privileged domain accounts facilitates lateral movement and large-scale distribution.
Group policies, scheduled tasks, remote services, SMB, WMI, and PowerShell are legitimate administrative resources that can be abused to spread the ransomware.
When domain controllers are affected, the company may also lose authentication services, name resolution, policies, and access to applications that depend on Active Directory.
Virtual machines and hypervisors
ESET research indicates the operation offers variants developed for Windows, Linux, and other platforms, as well as a C-based encryptor targeting VMware ESXi.
On Windows, the variant studied by Microsoft attempts to stop processes related to Hyper-V, such as vmms, vmwp, and vmcompute. Stopping these processes can free virtual disk files and allow them to be modified during encryption.
Potentially affected assets include:
- VMware virtual machines;
- Hyper-V servers;
- VMDK, VHD, and VHDX disks;
- virtual machine configurations;
- snapshots;
- datastore volumes;
- application files running inside VMs.
Compromise of a single hypervisor can leave multiple virtual machines unavailable at the same time.
Databases
The ransomware attempts to stop processes associated with SQL Server, MySQL, PostgreSQL, Oracle, and other platforms before encryption.
Stopping these services frees files that would normally be locked by the operating system. As a result, MDF, LDF, PostgreSQL databases, Oracle files, and other structures can be altered by the ransomware.
Even when encryption is partial, a database may fail to mount due to damage to headers, system pages, catalogs, indexes, or transaction logs.
Backup systems
The list of processes and services terminated by the variant includes components related to Veeam, Iperius, Commvault, and other backup and recovery solutions.
Attackers may also:
- delete shadow copies;
- erase or encrypt accessible repositories;
- compromise administrative credentials;
- change retention policies;
- delete snapshots;
- target servers that manage backups;
- use domain accounts to reach connected copies.
For this reason, the mere existence of a backup does not mean recovery can start immediately. First, its integrity, date, and the possibility that it contains malicious files or persistence mechanisms must be verified.
NAS, SAN, and RAID systems
NAS, SAN, DAS storages and RAID arrays can also be affected when their volumes are mounted on compromised servers or available via network shares.
The share-focused execution mode allows The Gentlemen to encrypt mapped drives and UNC paths. Consequently, data stored on external equipment can be altered even when the ransomware is not executed directly on the storage operating system.
Beyond file encryption, the incident may cause logical damage to file systems, volumes, virtual machines, and databases stored on these devices.
What should you do after a The Gentlemen attack?
Actions taken immediately after discovering the incident can increase or reduce the chances of recovery.
Isolate affected systems
Disconnect compromised equipment from the wired network, Wi‑Fi, and shares.
When multiple servers or subnets are being hit, isolation at the switch level may be necessary. The priority should be to prevent the self-propagation mechanism from reaching new devices.
CISA recommends identifying affected systems and isolating them immediately. If disconnecting them from the network is not possible, a shutdown can be considered to contain the spread, although this action will cause the loss of data present in volatile memory.
Do not reimage or reinstall immediately
Reinstalling the operating system, formatting volumes, and recreating arrays can overwrite important information.
Before any destructive change, preserve:
- samples of encrypted files;
- the ransom note;
- the added extension;
- logs;
- system memory;
- suspect executables;
- firewall records;
- disk images;
- information about compromised accounts and access.
CISA recommends capturing images of systems and memory, as well as preserving logs and other volatile artifacts used in the investigation.
Check whether the overwrite routine ran
The Gentlemen has a parameter that can instruct the overwriting of free space on volumes.
When this function is enabled, the malware creates a temporary file and writes random data until all available space is filled. It then deletes the file. The goal is to eliminate traces of deleted files, temporary copies, and unallocated content that could be found by forensic tools.
This routine can significantly reduce options based on recovering deleted files. Therefore, it is important to avoid new writes on affected disks.
Preserve the note and original files
Keep the README-GENTLEMEN.txt note, when present, and set aside samples of encrypted files of different sizes and formats.
Do not change extensions, do not edit contents, and do not run unknown tools repeatedly against the original files.
Samples should be copied for analysis, preserving the affected devices without further changes whenever possible.
Do not restore backups directly onto the compromised network
Backups should be examined in an isolated environment.
Restoring before eliminating the intruders’ access can allow the new environment to be compromised again. There is also a risk of restoring malicious tools, scheduled tasks, altered accounts, or configurations created during the intrusion.
It is recommended to maintain offline backups and regularly test their availability and integrity in disaster recovery scenarios. Restoration should be prioritized in a clean network, starting with the systems essential to operations.
Rotate credentials carefully
Administrative passwords, service accounts, VPN access, domain users, and backup credentials must be considered potentially compromised.
Rotation should occur from secure devices and as part of a coordinated plan. Changing only some passwords while intruders still have access to the network can alert them and accelerate ransomware deployment.
Is it possible to recover files encrypted by The Gentlemen?
The possibility of recovery depends on the variant, the parameters used, the systems affected, and the changes made after the attack.
There is no universal answer. Each incident must undergo a technical diagnosis.
Variant identification
The analysis starts by collecting:
- the added extension;
- the ransom note;
- file samples;
- the ransomware executable;
- the footer appended to files;
- logs and executed commands;
- the affected operating system;
- encryption characteristics.
In the variant studied by Microsoft, files contained an internal marker related to the name GENTLEMEN, as well as information required for potential cryptographic reconstruction by the criminals’ decryptor.
Because new versions may present different settings, the presence of the .umc16h extension should not be the sole identification criterion.
Partial encryption analysis
Larger files may have only certain regions encrypted. This speeds up the attack but does not mean the files can be opened normally.
In databases, virtual machines, and archives, small changes in critical regions can completely prevent access to the content.
Specialists can assess:
- which regions were altered;
- the position of encrypted segments;
- header integrity;
- the existence of unaffected pages or blocks;
- remaining metadata;
- internal copies;
- snapshots and transaction logs;
- consistency across disks and volumes.
In certain scenarios, it may be possible to reconstruct structures, extract consistent data, or recover usable parts. However, partial encryption is not a guarantee of recovery.
Virtual machine recovery
When VMDK, VHD or VHDX files are affected, the virtual machine may fail to boot even if most of the disk remains intact.
The work may involve:
- reconstructing the virtual disk descriptor;
- analyzing the snapshot chain;
- repairing the internal file system;
- extracting files directly from the virtual disk;
- recovering databases present on the VM;
- rebuilding the machine configuration;
- validating data before restoration.
The priority should be to recover the information, not simply to attempt to start a damaged virtual machine repeatedly.
Database recovery
Database files require specific analysis because they have complex structures and internal dependencies.
The process may include rebuilding pages, tables, indexes, catalogs, control files, and transaction logs.
Even if the database cannot be mounted by the original software, parts of the data may remain technically accessible. Feasibility depends on which regions were encrypted and the overall state of the files.
RAID, NAS, and SAN recovery
When ransomware hits data stored on RAID, NAS, or SAN, it may be necessary to reconstruct the storage structure first.
The analysis may involve:
- disk order and configuration;
- RAID parameters;
- file systems;
- logical volumes;
- LUNs;
- datastores;
- snapshots;
- virtual disks;
- databases;
- encrypted files.
Disks should not be reinitialized, rebuilt, or reinserted randomly into controllers. An incorrect rebuild can overwrite data and worsen the incident.
Case study: recovery after a The Gentlemen attack
The possibility of recovery is not limited to theoretical scenarios. Digital Recovery has worked directly on an incident involving The Gentlemen ransomware at a financial-sector company in Kenya.
The attack compromised a VMware virtual environment with more than 10 TB of critical data and left the company’s operations paralyzed. The scenario was even more complex because the intruders had deleted existing backups, eliminating the conventional restoration path.
The strategy was executed remotely, honoring the client’s requirement to keep data within its own infrastructure. Among the affected assets was the organization’s main database, which concentrated information essential to business continuity.
After diagnosis and recovery work, it was possible to recover the critical database and complete the project within a week, from case intake to final approval of the recovered data.
The incident shows that even in a The Gentlemen attack involving VMware, deleted backups, and large data volumes, technical recovery alternatives may still exist. Each case, however, must be analyzed individually.
Read the full case: Recovery of a critical database after a The Gentlemen ransomware attack in Kenya.
Does paying the ransom guarantee recovery?
No. Payment does not guarantee that criminals will deliver a working key, that the tool will recover all files, or that stolen data will be deleted.
The FBI does not recommend paying and warns that handing over the requested amount does not guarantee the organization will get its data back.
Even when a decryptor exists, problems can occur, such as:
- database corruption;
- virtual disk failures;
- very slow decryption;
- errors in large files;
- loss of metadata;
- unstable tools;
- lack of support;
- additional payment demands;
- subsequent publication of exfiltrated data.
Before making any decision, it is important to assess devices, backups, and available recovery alternatives from a technical standpoint.
How can you reduce the risk of new attacks?
Prevention needs to address initial access, lateral movement, and recovery capability.
Priority measures include:
- enforcing multi-factor authentication on VPNs, remote access, and administrative accounts;
- rapidly patching vulnerabilities in firewalls and edge devices;
- restricting administration panels exposed to the internet;
- reviewing privileged and service accounts;
- applying the principle of least privilege;
- segmenting users, servers, virtualization, storage, and backups;
- restricting SMB, WMI, WinRM, PsExec, and PowerShell;
- disabling SMBv1;
- monitoring remotely created tasks and services;
- enabling tamper protection in EDR;
- monitoring the loading of vulnerable drivers;
- maintaining offline or immutable backups;
- periodically testing restoration;
- protecting ESXi interfaces on an isolated management network;
- reviewing vendor and third-party access;
- maintaining an incident response plan.
Unit 42 recommends limiting lateral movement, restricting ESXi administration interfaces, enabling tamper protections in EDR, and validating offline backup and recovery capabilities.
It is also important to monitor behaviors, not just known files. The Gentlemen uses legitimate administration tools, modified scripts, and adapted variants during the intrusion. Controls based on signatures alone may be insufficient.
Data recovery after a The Gentlemen attack
An incident involving The Gentlemen requires coordination among information security, infrastructure, management, legal, business continuity, and data recovery specialists.
Digital Recovery works on the analysis and recovery of:
- physical servers;
- RAID systems;
- NAS, DAS, and SAN storage;
- VMware and Hyper-V virtual machines;
- Proxmox, Nutanix, and XenServer environments;
- SQL Server, Oracle, MySQL, MariaDB, and other databases;
- Windows and Linux systems;
- backup devices and repositories;
- files encrypted or corrupted by ransomware.
The technical diagnosis seeks to identify the variant, understand the encryption pattern, analyze the state of devices, and define which systems should be prioritized.
Recovery should be performed on controlled copies of devices whenever possible. Recovered data must be validated and transferred to a clean infrastructure, without reusing compromised credentials or configurations.
If you identify files encrypted by The Gentlemen, stop making changes to devices, preserve evidence, and seek specialized support. Random attempts at reinstallation, RAID rebuilds, or restoration may reduce the chances of recovery.
Frequently asked questions about The Gentlemen ransomware
Is The Gentlemen related to Qilin?
Public reports indicate that some operators may previously have acted as ArmCorp, a Qilin affiliate. This relationship is based on intelligence research and does not mean the two operations are currently the same group.
What extension does The Gentlemen add to files?
The sample analyzed by Microsoft added the .umc16h extension. However, the extension may vary depending on the version and the configuration used by the affiliate.
What is the ransom note called?
In the variant documented by Microsoft, the note was called README-GENTLEMEN.txt. Other campaigns may use different names.
Is there a free decryptor for The Gentlemen?
You should not assume there is a public tool compatible with all variants. The version must be identified and recognized solutions checked before running any decryptor.
Does The Gentlemen target VMware ESXi?
Yes. ESET research identified a C-written variant targeting ESXi environments, in addition to encryptors for Windows, Linux, and other platforms.