
Qilin ransomware is one of the most active and well-structured ransomware operations in the market. Initially known as Agenda, the group operates under the Ransomware-as-a-Service, or RaaS, model, providing its infrastructure and tools to affiliates responsible for breaching companies, stealing information, and encrypting systems.
The threat is not limited to users’ computers. Qilin variants have been developed to target Windows, Linux, and VMware ESXi environments, allowing attackers to compromise servers, virtual machines, network shares, databases, and backup systems. MITRE ATT&CK reports that the ransomware family has been active since at least 2022 and includes versions developed in Go and Rust.
The operation has continued to show a high level of activity in recent years. In the second quarter of 2025, Qilin accounted for 24% of the ransomware incidents reported to MS-ISAC involving state, local, tribal, and territorial governments in the United States. In the second quarter of 2026, it was also identified as the most active group monitored by Group-IB in the Australia and New Zealand region.
For affected companies, understanding how the ransomware works is only one part of the process. It is also necessary to contain the incident, preserve evidence, and technically assess the possibilities for recovering data encrypted by Qilin.
What is Qilin ransomware?
Qilin is a ransomware family associated with a criminal operation that uses the RaaS model. Under this model, the operators maintain the malware, communication infrastructure, leak site, and negotiation mechanisms, while affiliates carry out the attacks against organisations.
This structure allows different attackers to use the same ransomware while adopting different methods for initial access and lateral movement within the network. As a result, two attacks attributed to Qilin may involve different intrusion paths, tools, and levels of impact.
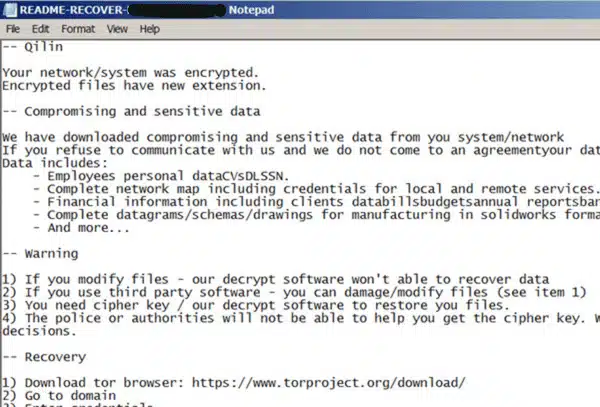
The group also uses a double extortion strategy. Before encrypting files, attackers may copy documents, databases, personal information, and other confidential content. After the attack, the victim is pressured to pay both for the supposed decryption and for the promise that the stolen data will not be disclosed.
The theft of information significantly increases the impact of the incident. Even when an organisation has viable backups, it may still face legal, regulatory, financial, and reputational risks resulting from data exposure.
Initially identified as Agenda, the ransomware later became widely associated with the name Qilin. Although both names still appear in technical reports, they generally refer to the same ransomware family or to the evolution of the same operation.
How does a Qilin ransomware attack happen?
A Qilin attack does not necessarily begin with encryption. In many incidents, attackers remain inside the infrastructure for some time, analysing the network, gaining privileges, and identifying the most critical assets before deploying the ransomware.
Initial access
Initial access can occur through several different methods, including:
- phishing emails containing malicious links or attachments;
- compromised credentials;
- exposed RDP interfaces;
- vulnerable applications accessible from the internet;
- remote access services;
- administrative accounts without multi-factor authentication.
MITRE ATT&CK associates Qilin with the use of phishing, exploitation of exposed applications, RDP, Citrix, and other remote access tools.
Reconnaissance and credential theft
After gaining access to the environment, the attackers seek to identify users, servers, domain controllers, network shares, virtual systems, and backup mechanisms.
Qilin and its affiliates may use PowerShell, legitimate administrative tools, and utilities such as Mimikatz to obtain credentials and elevate their privileges. Compromised administrative accounts allow attackers to access different network segments and modify domain policies.
Lateral movement
With sufficient privileges, the operators can distribute malicious tools and files across systems. Techniques involving PsExec, SMB, SSH, scripts, scheduled tasks, and group policies may be used to execute the ransomware simultaneously across multiple systems.
This stage explains why some attacks can quickly affect workstations, servers, virtual machines, and shared volumes.
Compromise of recovery mechanisms
Before encryption, attackers may attempt to delete shadow copies, stop services, restart backup servers, or modify virtual environment configurations.
In VMware infrastructures, techniques attributed to Qilin include identifying ESXi hosts and vCenter clusters, shutting down virtual machines, and removing snapshots. There are also reports of actions taken to disable high-availability features and make recovery more difficult.
Exfiltration and encryption
After identifying the most important data, the attackers may transfer information to external servers. Large-scale encryption typically occurs only after this stage.
Qilin variants may use symmetric algorithms, such as AES or ChaCha20, to encrypt data, while RSA keys are used to protect the keys involved in the process. The configuration may vary between campaigns and affiliates.
At the end of the process, the ransomware adds extensions to the affected files and leaves ransom notes with contact instructions. Because Qilin is configurable, both the file extension and the name of the ransom note may vary from one attack to another.
Which systems can be affected by Qilin?
Qilin poses a particularly significant threat to businesses because of its cross-platform capabilities. Its impact is not limited to files stored on Windows computers.
Windows servers and Active Directory
File servers, domain controllers, ERP systems, corporate applications, and SMB shares can be compromised once attackers obtain administrative privileges.
Compromising Active Directory allows attackers to distribute commands, modify policies, and expand the reach of the attack across the organisation.
Linux and database environments
Linux variants can target directories associated with enterprise services, containers, virtualisation, and databases.
Technical analyses have identified paths related to MySQL, PostgreSQL, MongoDB, Redis, Elasticsearch, Docker, VMware, Xen, and other services among the targets scanned by the ransomware.
VMware ESXi and virtual machines
VMware ESXi servers are important targets because they host multiple virtual machines within a single environment. If the ransomware succeeds in encrypting datastores or virtual disks, several services can become unavailable at the same time.
VMDK files, virtual machine configurations, snapshots, and VMFS structures can be affected. Broadcom has already published a specific alert about a Linux variant of Qilin targeting VMware ESXi environments.
NAS, SAN, and RAID systems
NAS and SAN storage systems, as well as RAID volumes, can be affected when they are accessible from compromised servers or when attackers gain administrative access to the devices.
Even if the ransomware is not executed directly on the storage system, stored files can still be encrypted through network-mounted shares. In some cases, the logical structure of the volume, snapshots, and backup copies may also be compromised.
Backup systems
Attackers seek to reduce recovery options before revealing the attack. For this reason, backup servers, repositories, administrative credentials, and management consoles should also be included in the investigation.
Backups that remain permanently connected to the domain can be deleted, encrypted, or altered. The existence of a backup does not automatically mean that it is intact, up to date, and free from the mechanisms used during the intrusion.
The impact of a Qilin attack

One of the best-known incidents associated with Qilin affected Synnovis, a company that provides laboratory and pathology services to organisations connected to the United Kingdom’s public healthcare system.
The attack, identified in June 2024, disrupted laboratory services and led to the postponement of procedures and appointments at hospitals in London. Synnovis stated that the investigation was carried out with support from organisations including the National Crime Agency, NHS England, and the National Cyber Security Centre.
The case demonstrates that the impact of ransomware goes far beyond file loss. System downtime can disrupt critical operations, prevent access to essential information, and affect customers, patients, suppliers, and partners.
The main consequences of a Qilin attack include:
- disruption of operations;
- unavailability of servers and virtual machines;
- loss of access to databases;
- compromise of backups;
- leakage of confidential information;
- disruption of production systems;
- legal and regulatory costs;
- damage to the company’s reputation;
- increased time required for operational recovery.
What to do after a Qilin ransomware attack?
The first decisions made after discovering the attack can directly influence the chances of recovery. The priority should be to contain the spread without destroying important evidence.
Isolate the affected systems
Disconnect compromised devices from the network and interrupt communication between affected segments. When multiple devices are being encrypted, it may be necessary to block connections at the switch level or isolate entire sections of the infrastructure.
CISA recommends identifying affected systems and isolating them immediately. Shutting down the system should be considered primarily when it is not possible to disconnect the device from the network, as important information may temporarily reside in memory.
Do not format or reinstall the servers
Formatting disks, reinstalling operating systems, or recreating volumes can overwrite structures that are important for the investigation and data recovery.
Even files that appear unusable may contain recoverable data. Changes made without prior analysis can reduce the available technical recovery options.
Preserve the evidence
Keep copies of ransom notes, file extensions added to affected files, logs, encrypted files, malware samples, and security system records.
It is also important to document when the incident was identified, which devices were affected, and what actions have already been taken.
CISA recommends preserving system images, memory, security logs, and firewall records during the response to ransomware incidents.
Do not run random decryption tools
An incompatible tool may modify files, cause further corruption, or make a subsequent recovery attempt more difficult.
The correct identification of the ransomware family, variant, and encryption behaviour should take place before using any tool. The No More Ransom project provides Crypto Sheriff to help identify the ransomware and check for available public solutions.
Analyse backups in an isolated environment
Do not immediately reconnect backups to the compromised infrastructure. They should be checked in a controlled environment to confirm that they are intact and do not contain malicious files, compromised accounts, or persistence mechanisms.
Restoring the entire environment without eliminating the attackers’ access may allow another attack to occur.
Is it possible to recover data encrypted by Qilin?
Recovery depends on the variant used, how the encryption was carried out, the systems affected, and the actions taken after the incident.
It should not be assumed that there is a universal public tool capable of decrypting all Qilin variants. Each attack must be analysed individually.
Recovery may involve different approaches:
Identification of the variant
The analysis begins with the extension added to the files, the ransom note, malware samples, and the behaviour observed across the affected systems.
This information helps identify the variant and determine how the data was processed.
Encryption analysis
Specialists can assess how the ransomware processed the files, which algorithms were used, whether the encryption was complete or partial, and whether any failures occurred during execution.
In some scenarios, interruptions in the encryption process, implementation errors, or temporary files may create recovery opportunities. This does not occur in every case and can only be confirmed after a diagnostic assessment.
Recovery of storage structures
Even when the files are encrypted, it may first be necessary to rebuild the logical infrastructure where they were stored.
Digital Recovery specialises in data recovery from:
- physical servers;
- NAS, DAS and SAN storage systems;
- RAID systems;
- VMware and Hyper-V virtual machines;
- SQL Server, Oracle, MySQL, and other databases;
- backup systems;
- Windows and Linux volumes.
The analysis may include virtual disks, file systems, damaged volumes, corrupted databases, and remaining copies found on the devices.
Restoration in a secure environment
Recovered data should be validated and transferred to a clean infrastructure. Restoration should follow a defined order based on system criticality and the dependencies between applications, databases, and services.
The goal is not only to recover individual files, but to enable the company to resume operations securely.
Does paying the ransom guarantee recovery?
Paying the ransom does not guarantee that the attackers will provide a working decryption key, that all files will be recovered, or that stolen data will be deleted.
CISA itself warns that paying the ransom does not guarantee that access to systems and data will be restored.
Even when the attackers provide a decryption tool, problems may still occur, such as:
- extremely slow decryption;
- extremely slow decryption;
- failures when decrypting large databases;
- virtual machines that fail to boot;
- loss of metadata;
- lack of technical support;
- another extortion attempt;
- subsequent disclosure of stolen information.
Before considering any negotiation, the organisation should technically assess the data, backups, and compromised devices. In many cases, there are recovery alternatives that do not depend on paying the attackers.
How to reduce the risk of future attacks?
Preventing Qilin attacks requires controls capable of blocking initial access, limiting lateral movement, and protecting recovery mechanisms.
The most important measures include:
- multi-factor authentication for VPNs, remote access, and administrative accounts;
- updating systems, hypervisors, firewalls, and exposed applications;
- segmentation between users, servers, storage systems, and backups;
- application of the principle of least privilege;
- application of the principle of least privilege;
- monitoring of PowerShell, PsExec, RDP, SMB, and SSH;
- EDR and XDR on servers and endpoints;
- monitoring of Windows, Linux, and virtualised environments;
- offline, isolated, or immutable backups;
- regular restoration tests;
- incident response plan;
- anti-phishing training.
Security solutions must also monitor cross-platform behaviour. Trend Micro researchers identified an Agenda/Qilin campaign that used a Linux variant within Windows systems, demonstrating how operators continue to adapt their techniques to evade traditional detection mechanisms.
Data recovery after a Qilin attack
A Qilin ransomware attack requires a coordinated response involving information security, IT infrastructure, legal, risk management, and data recovery specialists.
Digital Recovery has extensive experience in analysing and recovering servers, RAID systems, storage systems, virtual machines, databases, and backups affected by ransomware.
Each incident is assessed individually to identify the variant, understand the extent of the encryption, and determine the safest technical recovery options. The diagnostic assessment helps prevent attempts that could worsen the damage and allows essential systems to be prioritised to ensure business continuity.
If you identify files encrypted by Qilin, stop making changes to the affected devices and seek specialist assistance. The less the infrastructure is altered after the attack, the greater the chances of preserving important information for recovery.
Frequently asked questions about Qilin ransomware
Are Qilin and Agenda the same ransomware?
Agenda was the name initially associated with the ransomware family. As the operation evolved, the name Qilin became more widely used. Technical reports may still refer to both names.
What extension does Qilin add to files?
There is no single extension used in every attack. Qilin supports different configurations, and the extension may vary depending on the campaign and the affiliate responsible for the intrusion.
Is there a free decryptor for Qilin?
The availability of a decryption tool must be checked according to the specific variant. A decryptor should not be run before confirming that it is compatible with the affected files.
Does Qilin target VMware ESXi servers?
Yes. There are Linux variants and techniques associated with compromising VMware ESXi and vCenter environments. Virtual disks, datastores, snapshots, and virtual machine configurations may be affected.
Is it possible to recover data without a backup?
In some cases, recovery may be possible through the analysis of devices, file systems, databases, volumes, and remaining data structures. The outcome depends on the specific circumstances of the incident and cannot be guaranteed without a diagnostic assessment.
Does Qilin also steal data?
Yes. The operation uses double extortion, combining encryption with data theft. Therefore, the response should address both operational recovery and the investigation of a potential data breach.
Should I shut down the affected servers?
The priority is to isolate them from the network. Shutting them down may eliminate temporary information that could be important for the investigation, but it may be necessary when there is no other way to prevent the attack from spreading. The decision should take into account the current state of the attack and, whenever possible, be made with specialist guidance.
Should I pay the ransom?
Payment does not guarantee complete decryption or prevent the disclosure of stolen data. Before making any decision, it is advisable to carry out a technical assessment of the available recovery options.


